CI GATE
Stop risky releases automatically
Enforce your security requirements directly in your CI/CD pipeline and prevent builds with non-compliant vulnerabilities from progressing.
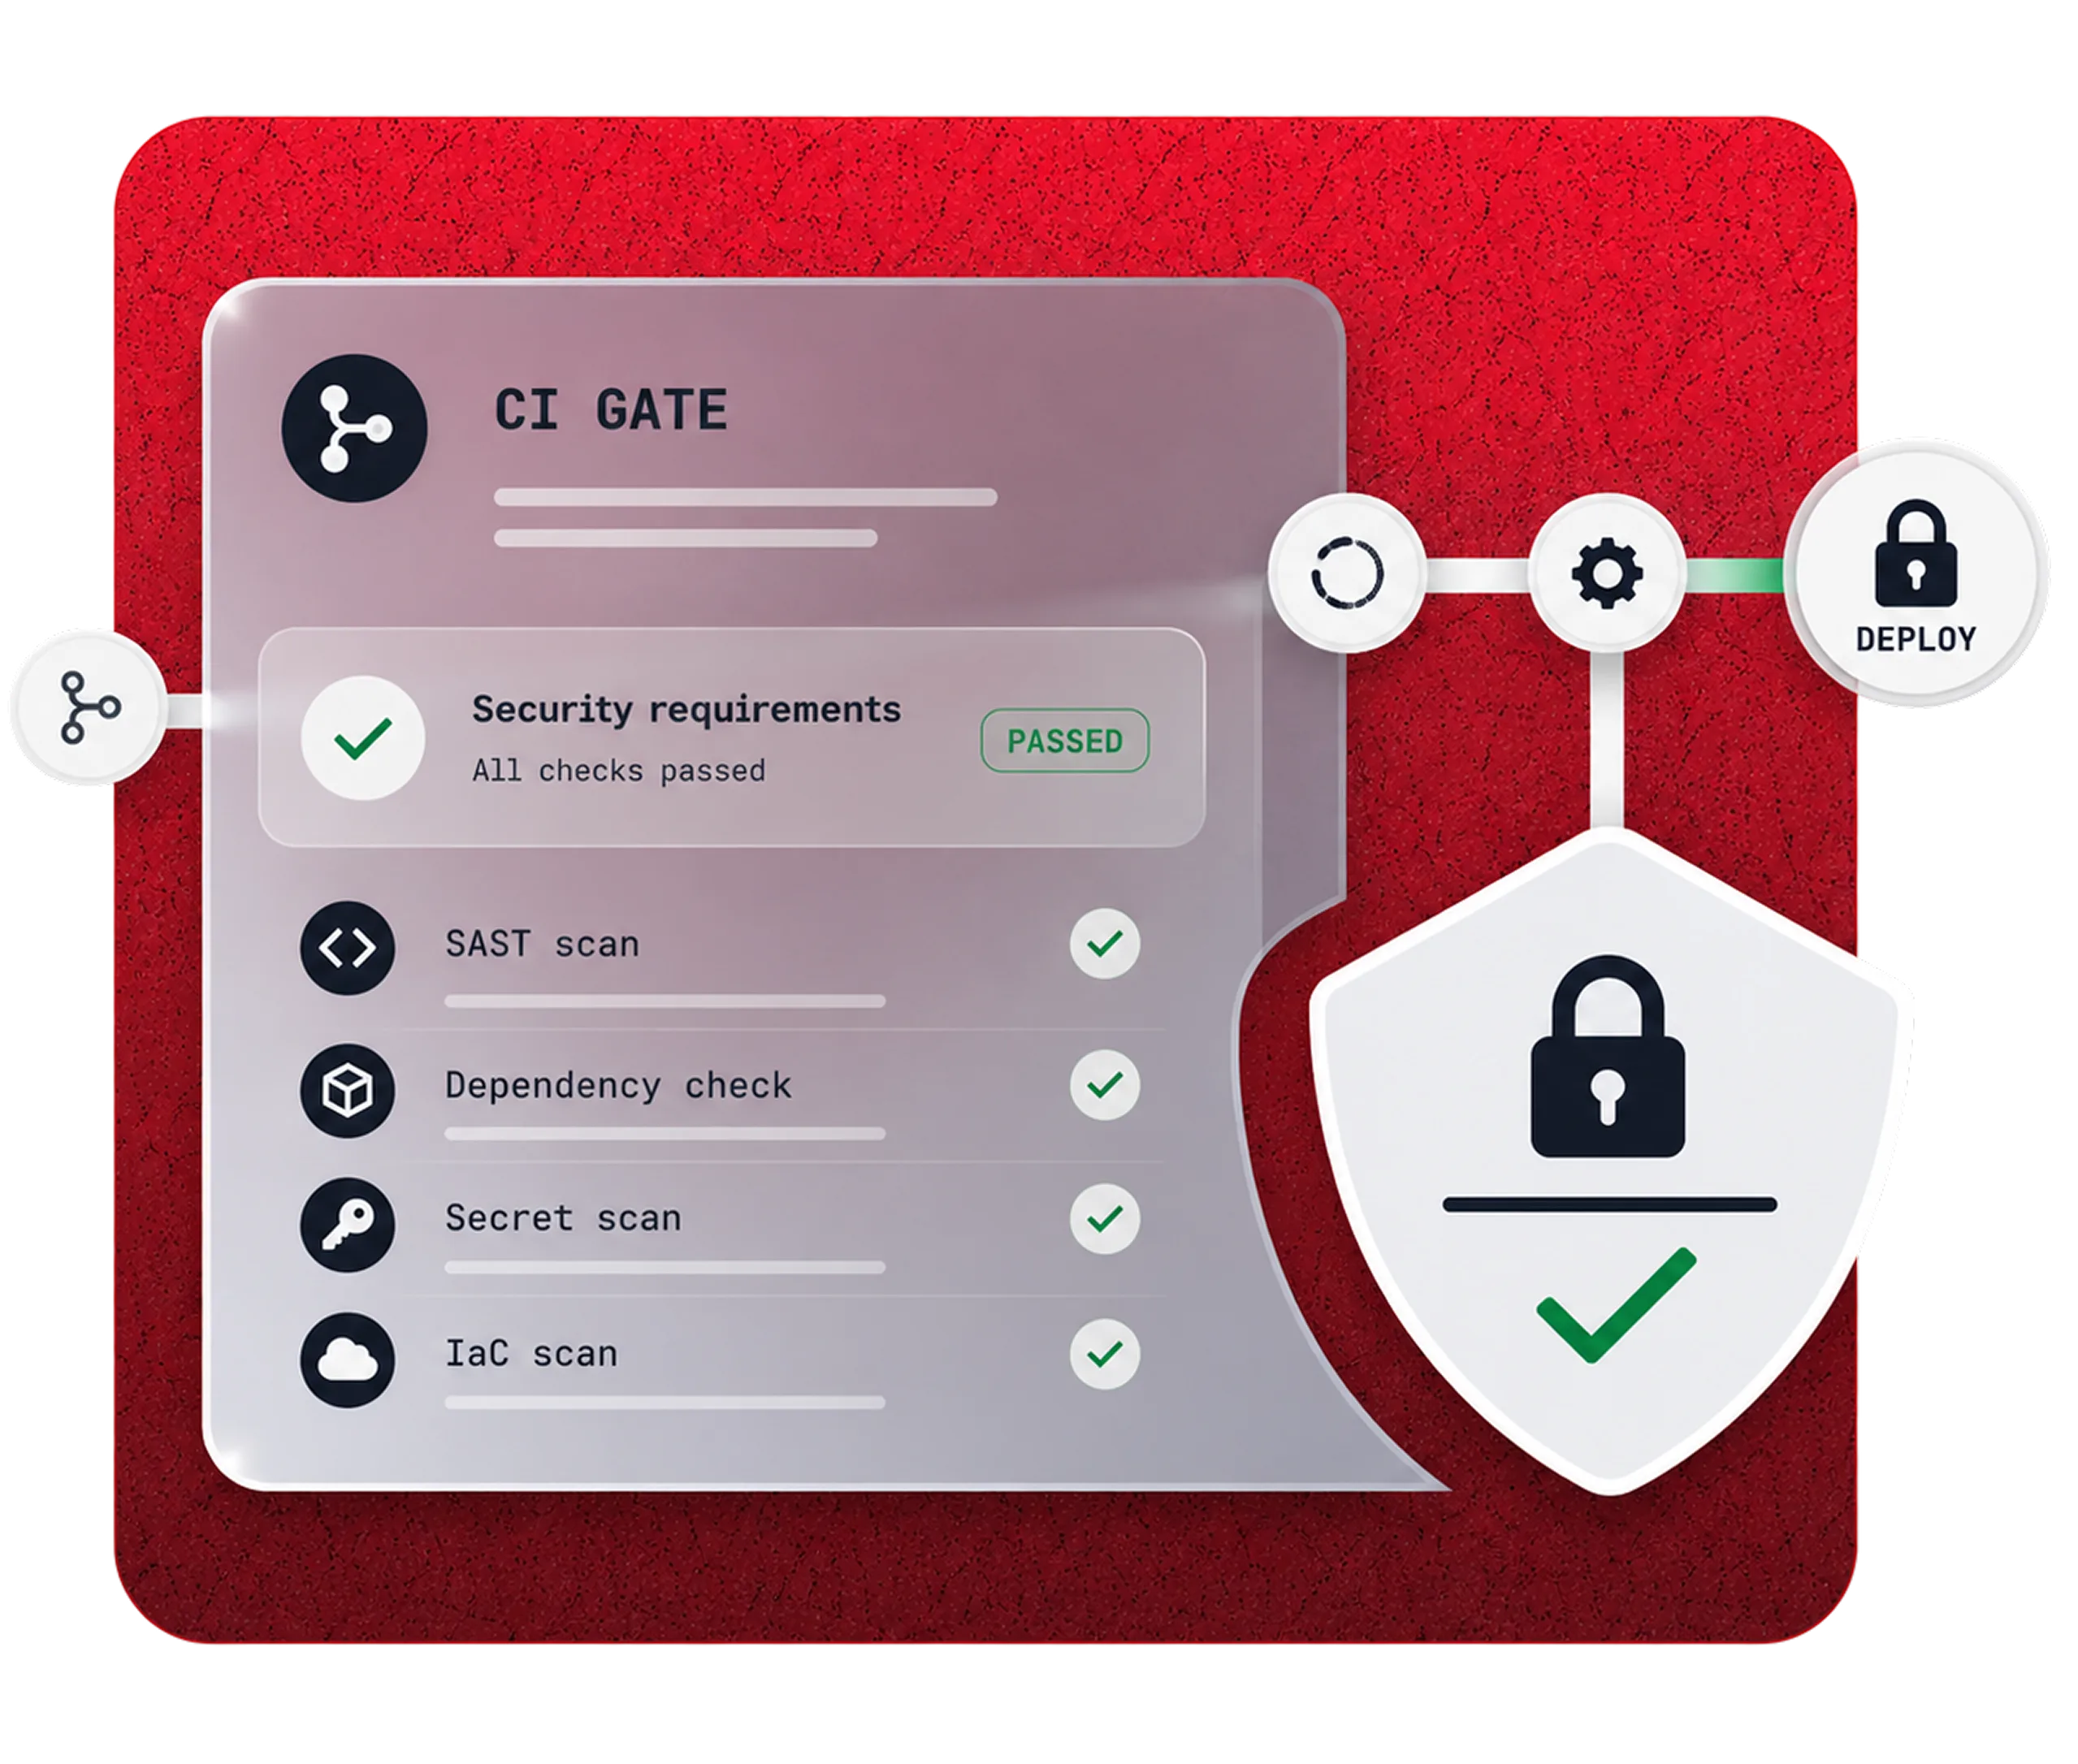
Turn security policies into release controls
CI Gate evaluates vulnerabilities against your organization's security policies and automatically prevents non-compliant builds from progressing.
Apply policies
Compare vulnerabilities against your organization's security requirements, severity thresholds, and grace periods.
[ KEY BENEFITS ]
Ship with security built in
Make security requirements part of your release process and prevent known risks from reaching production.

Security thresholds
Define which vulnerabilities can block a build.
Policy enforcement
Apply consistent security requirements across repositories.
Automatic release controls
Block or allow builds based on security results.
Reduced human error
Enforce security requirements automatically.
Faster release decisions
Get immediate feedback before software is released.
Works with your CI/CD
Integrate with GitHub, GitLab, Azure DevOps, Jenkins, Bitbucket, and Harness.
One continuous security loop
From prevention to remediation.
SUPPORT
CI Gate is a core part of our solution
We offer an all-in-one solution that combines our platform, AppSec tools, AI, and our team of pentesters to help you continuously improve your cybersecurity posture.